DNS Propagation Explained: Why DNS Changes Take Time and How to Check Them
DNS Propagation Explained: Why DNS Changes Take Time and How to Check Them
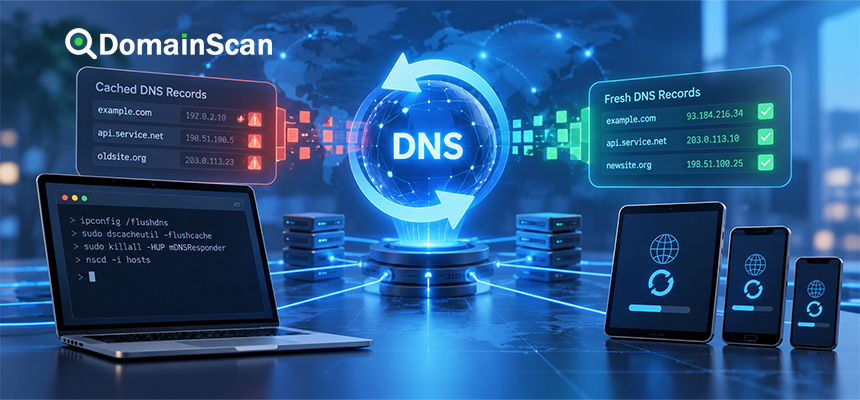
When you change a DNS record, nothing is actually “propagating” across the internet. Your new record is live on your nameservers the moment you save it. What takes time is for the thousands of DNS resolvers around the world to forget the old answer they cached earlier.
How long that takes is set mainly by one number: the TTL (time to live) of the old record. Once you understand TTL, you can predict how long a change will take, and in most cases make it take minutes instead of days.
How a DNS answer gets cached
When someone visits your site, their device does not ask your nameserver directly. It asks a recursive resolver, usually run by their ISP or by a public service such as Google Public DNS or Cloudflare’s 1.1.1.1. That resolver finds the answer from your authoritative nameserver and then keeps a copy.
Every DNS record carries a TTL in seconds. It tells the resolver how long it may reuse its copy before asking again. A record with a TTL of 3600 can be served from cache for up to one hour.
This is why people in different places see different results after a change. A resolver that cached your old record five minutes ago will keep serving it until its TTL runs out. A resolver that had no copy fetches the new one straight away.
The rule that predicts the wait
For an ordinary record change, the longest anyone should see the old value is roughly the TTL the old record had when it was last cached. The new record’s TTL does not matter for this change, only for the next one.
For example, if your A record had a TTL of 86400 (24 hours) and you change the IP address, some visitors may reach the old server for up to 24 hours. If the old TTL was 300, the switch is effectively complete within about 5 minutes.
Record changes vs nameserver changes
There are two very different kinds of DNS change, and they wait on different TTLs.
Changing a record inside your zone (A, AAAA, CNAME, MX, TXT) depends only on the TTL you set on that record. You control it completely.
Changing your nameservers at the registrar is slower. It updates the delegation records held by the top-level domain’s registry, and those have their own TTL, which you do not control. At the .com and .net registry, delegation NS records are published with a TTL of 172800 seconds, or two days. That figure is the real origin of the familiar advice to “allow up to 48 hours”.
In practice it is often faster. Many large resolvers cap long NS TTLs at a lower value, and some prefer the NS records published in your own zone over the parent’s. But for a nameserver move you should still plan for the full two days and keep both old and new DNS providers serving identical records throughout.
| Type of change | What sets the wait | Who controls it | Typical wait |
|---|---|---|---|
| A / AAAA / CNAME record | TTL of the old record | You | Minutes to 24 hours |
| MX record (email routing) | TTL of the old MX record | You | Usually 1 hour or less with default TTLs |
| TXT record (SPF, DKIM, DMARC, site verification) | TTL of the old record, or negative caching if the record is new | You | Minutes to 1 hour |
| Nameserver change at the registrar | TLD registry’s delegation TTL | The registry | Up to 48 hours for .com and .net |
The trap of a brand-new record
A new record can also be slow, for a less obvious reason. If anyone looked up the name before you created it, their resolver received a “does not exist” answer. Resolvers cache those negative answers too.
How long they keep them is set by the SOA record of your zone, as defined in RFC 2308. Many zones use values between 1 and 3 hours. So if you test a subdomain, see it fail, then create the record, your own resolver may keep reporting that it does not exist until that negative cache expires.
The fix is simple: create the record first and test afterwards.
How to make a DNS change take minutes
- Lower the TTL in advance. At least one full old-TTL period before the change, reduce the record’s TTL to 300 seconds. If the current TTL is 86400, do this a day ahead.
- Make the change. Because resolvers now hold the record for at most 5 minutes, almost everyone sees the new value within minutes.
- Keep the old target running. Leave the old server, or the old mail server for an MX change, working until the old TTL has passed. Visitors still holding the old answer will not hit a dead end.
- Raise the TTL again. Once everything is confirmed, set the TTL back to a normal value such as 3600. Very low TTLs increase query load and slightly slow first visits.
For a nameserver move, you cannot lower the registry’s TTL. The equivalent step is to set up every record on the new provider first, check it, and only then switch nameservers at the registrar.
How to check whether your change is live
Do not judge a change by refreshing your browser. Your browser, your operating system and your router may all hold their own cached copies. Check the DNS directly instead.
- Look up the record with the DomainScan DNS lookup tool. Choose the record type you changed, for example A, MX or TXT.
- Compare the returned value with what you entered at your DNS provider. If it matches, the authoritative data is correct and anything else is only caching.
- Note the TTL shown in the result. It tells you the longest a resolver should keep that answer before checking again.
- For a nameserver change, look up the NS records and confirm they list your new provider’s nameservers.
If the tool shows the old value from your authoritative nameservers, the problem is not propagation at all. The change was saved in the wrong place, usually at a DNS provider your domain is no longer using. Check which nameservers the domain points to and edit the records there.
Quick answers
Can I force DNS propagation? No. You cannot clear other people’s resolver caches. You can only shorten the wait by lowering TTLs before the next change.
Why does my site work on mobile data but not on Wi-Fi? The two networks use different resolvers, and one of them still holds the old record. Flushing your computer’s DNS cache can help locally, but the network’s resolver will refresh only when its TTL expires.
Is 48 hours always the rule? No. That figure applies to nameserver changes on .com and .net. Ordinary record changes follow your own TTL and are usually much quicker.